FDA Pentest for 510(k) Submissions. Submission-Ready in 48 Hours.
StealthNet delivers an FDA pentest for connected devices, companion apps, and backend APIs, with reports mapped to FDA premarket guidance and AAMI TIR57 and delivered in as little as 48 hours. Submission-ready hybrid (AI + human) engagements are a fixed fee of $5,000 to $10,000. For deeper background on scoping, read our medical device penetration testing guide, or see all penetration testing services.
First report in 48h · $5,000 to $10,000 fixed fee · Free remediation retest
FDA submissions without penetration test evidence face Refuse to Accept decisions. Most engagements can start within 24 hours.
Get Scoped in 24 Hours
Sample reportShare a few details and pick a time to chat right after.
Rather skip the form?
Book a 30-minute scoping call insteadTrusted by Companies Where Security Isn't Optional
What customers say
Highly recommend StealthNet AI
"StealthNet AI performed a thorough and comprehensive pen test, fast turnaround on conducting the test, they were very responsive, and it was great value."
Richard B.
Founder · Avara Software · Health, Wellness & Fitness
The best choice for penetration testing
"The testing was thorough and the reports were structured precisely for the regulatory requirements. Explanation of issues along with steps to reproduce and remediation advice were detailed and clear, making corrections a breeze."
Jeremy M.
Director · IKO Corp · Medical Devices
Scope starts with the threat model.
Why FDA reviewers look at your threat model before they look at your findings, and how we build one for connected devices, companion apps, and backend APIs.
From device scope to 524B-ready evidence in days
Scope the device, cloud, and mobile companion, AI agents map the attack surface, a senior tester confirms exploitability, and you receive an FDA premarket-ready package.
Confidential · Sample
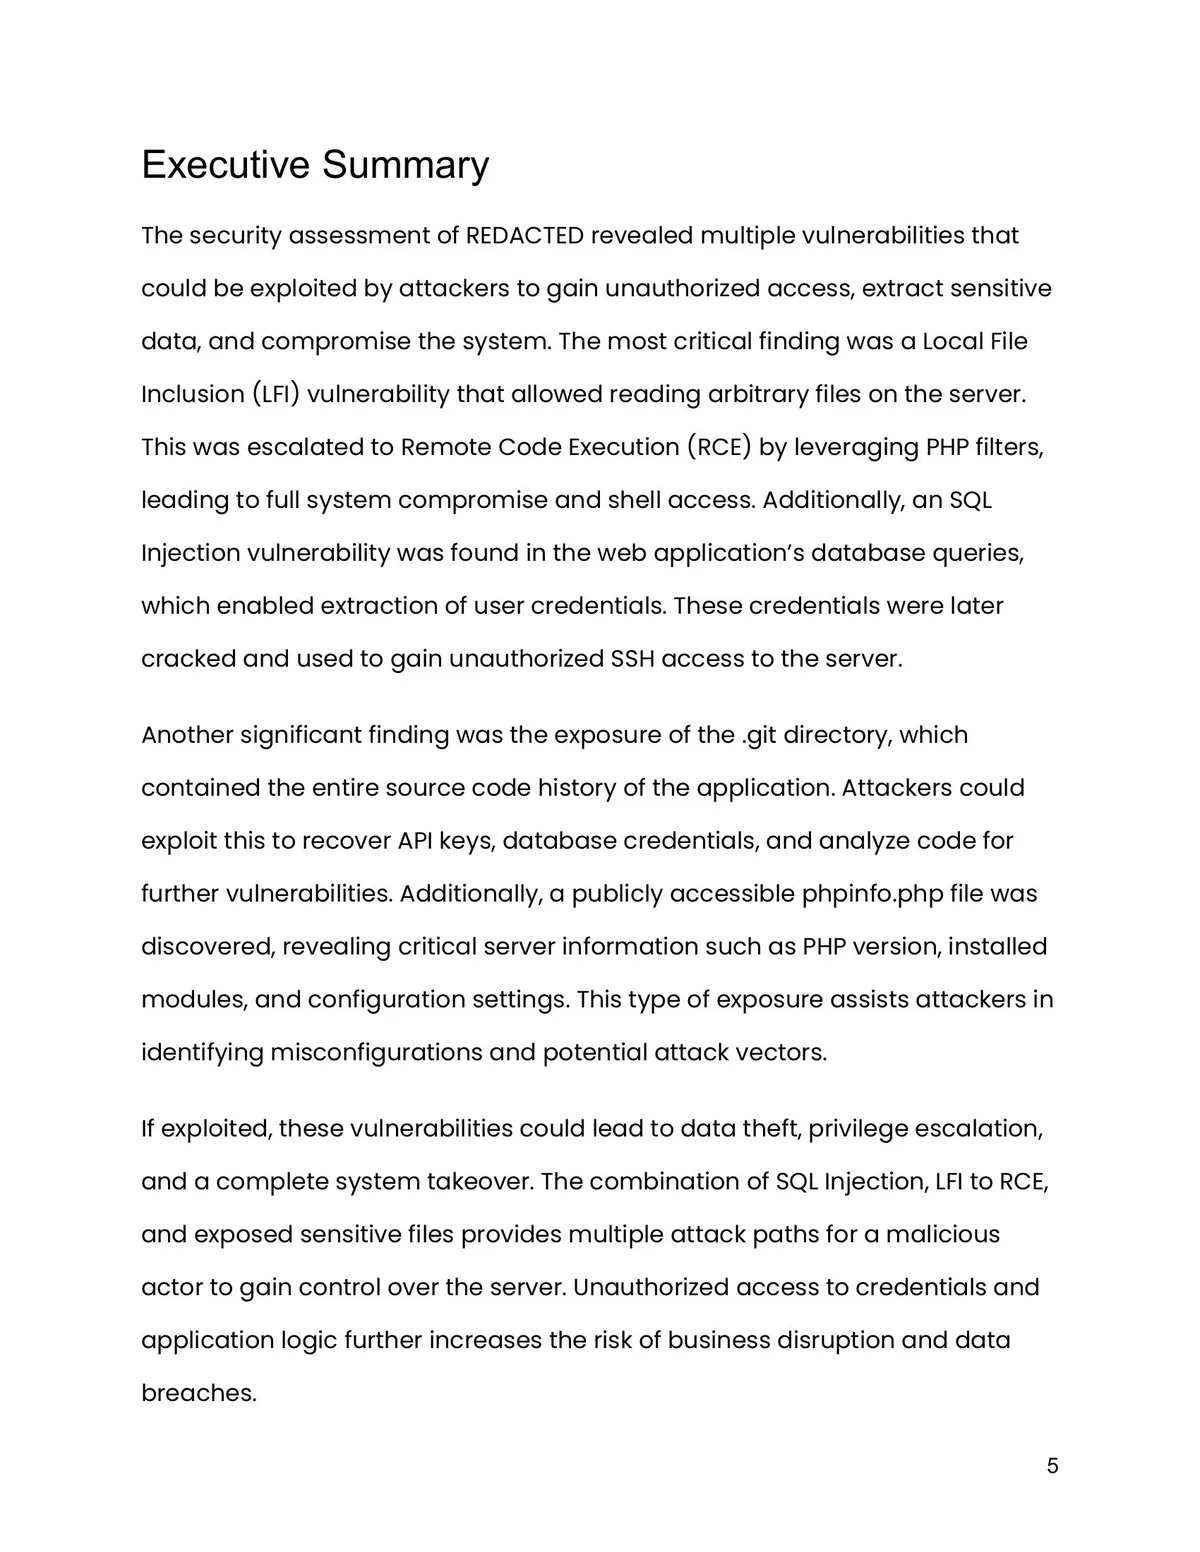
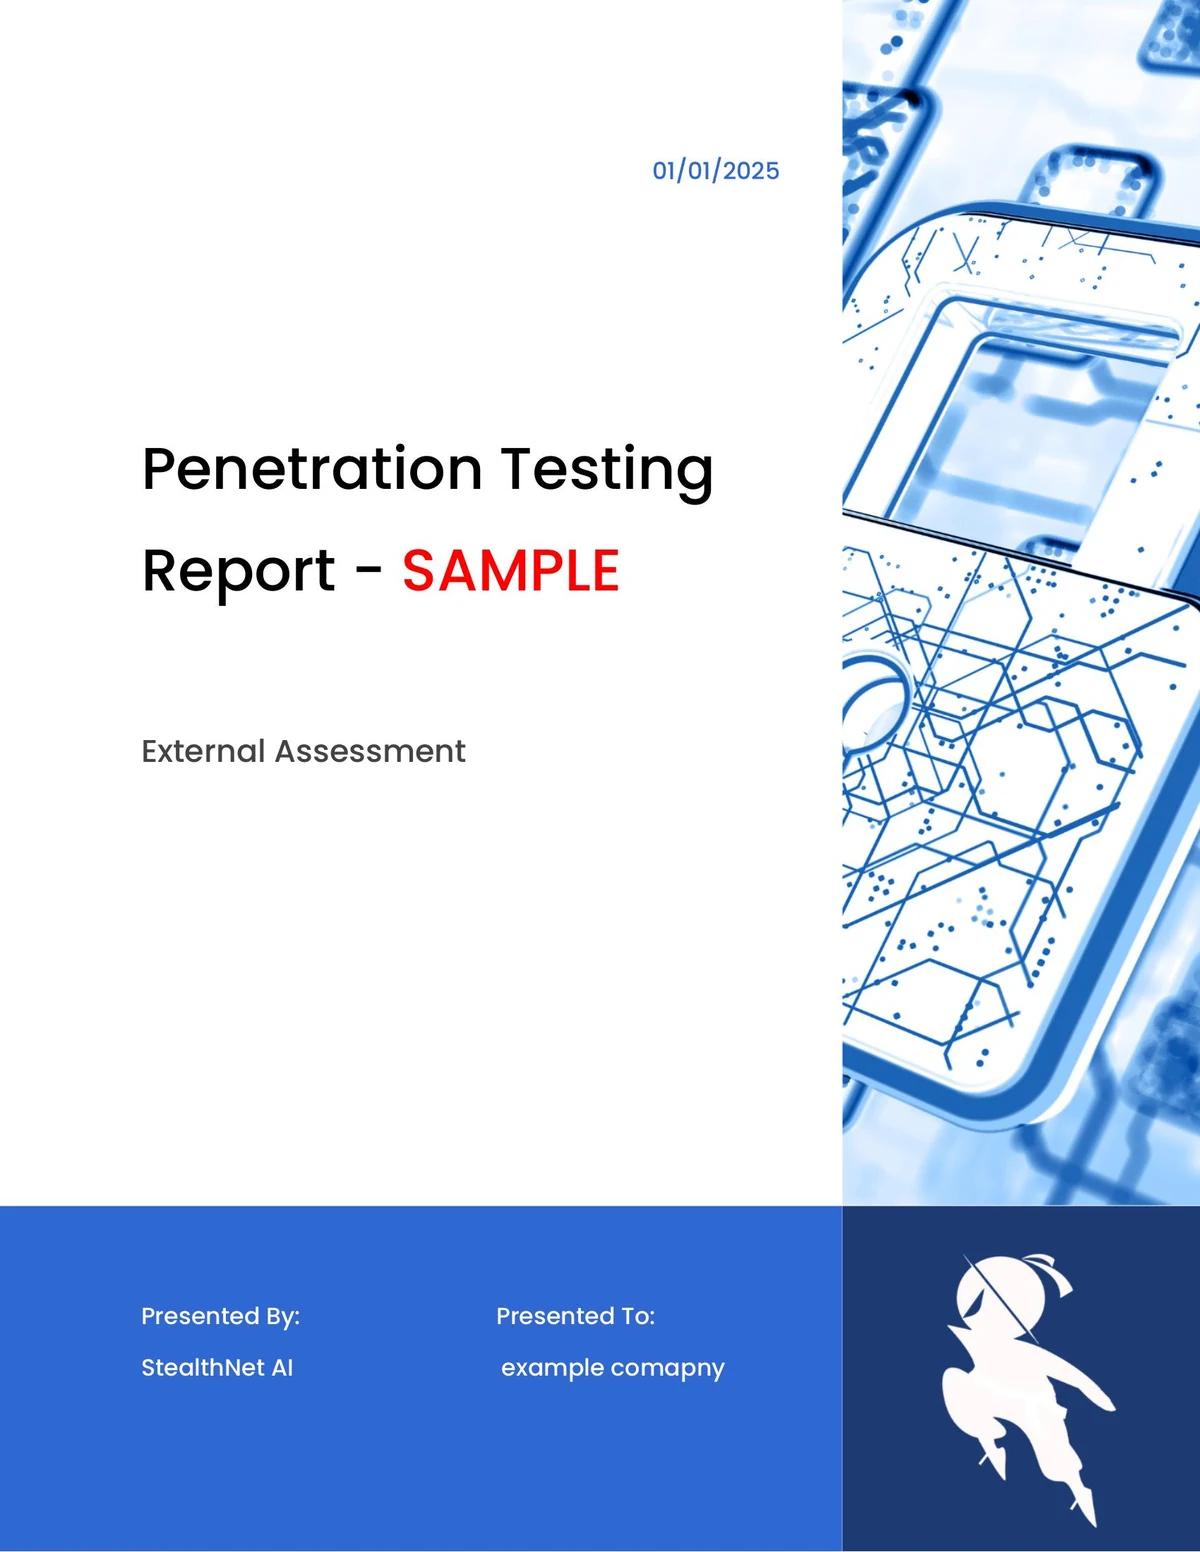
From kickoff to auditor-ready report, delivered in 48 hours.
Connected Devices Are Under Attack.
FDA rejects your submission
The FDA's 2023 premarket guidance now requires cybersecurity testing evidence. Submissions without penetration test results face Refuse to Accept (RTA) decisions.
Patient safety is at stake
Vulnerabilities in medical devices can directly impact patient health. Proactive testing prevents potentially life-threatening security incidents.
Specialized testing is expensive
Medical device security firms charge $30K to $80K for comprehensive testing. StealthNet delivers a submission-ready hybrid engagement for a fixed $5,000 to $10,000.
Penetration Testing for Medical Devices
Hybrid FDA Pentest (AI + Human)
$5,000 to $10,000
Fixed fee, quoted before any work begins
- AI attack simulation plus senior US-based pentester validation
- Device, companion app, and API surface
- Submission-ready report mapped to FDA premarket cybersecurity guidance
- ISO 14971 and IEC 81001-5-1 framing
- Dedicated project manager and private Slack channel
- Free retest included
Best for: Premarket 510(k) and PMA submissions, MDR technical documentation, device and companion app testing
StealthStrike (Baseline Testing)
$1,500
Not submission evidence. See the note below.
- 48-hour delivery, AI-only testing
- Exploit-validated findings
- Companion app and API surface coverage
- Useful between formal engagements
Best for: Post-market monitoring, interim testing between submissions, internal baseline
What moves the number
Single application
One API or one companion app, one role. Lands near the bottom of the range.
Multi-component submission
Inference or device API, plus the model or firmware layer, plus a containerized or on-premise deployment package. This is the most common 510(k) scope and lands near $7,500.
Multi-device program
Several devices or a full product family. Quoted above the range.
Most 510(k) submissions we test are multi-component. You get a fixed fee before any work starts, so the number on your SOW is the number you pay.
Which one does the FDA actually expect?
A 510(k) or PMA cybersecurity submission needs testing performed and documented by a qualified third party, with named human testers accountable for the findings. StealthStrike is AI-only, so we do not put it forward as submission evidence and we will tell you so on the call. Use it for post-market monitoring or a baseline read between formal engagements. For anything going in front of a reviewer, start with Hybrid.
Mapped to FDA Cybersecurity Guidance.
Device Security
Testing of device firmware, communication protocols, and physical interfaces
Backend & Cloud
Assessment of cloud APIs, data storage, and device-to-server communications
SBOM Validation
Software composition analysis and known vulnerability identification
Data Integrity
Testing of patient data protection, encryption, and access controls
AI Handles Speed. Humans Validate Everything.
A named, US-based senior tester validates every finding before your report is delivered.
Reports are mapped to FDA premarket guidance and AAMI TIR57, ready for your submission package.
Most clients receive their first report within 48 hours of scoping call completion.
Medical device companies and SaMD teams have used StealthNet to support 510(k) submissions.
FDA Pentesting Questions
Other Compliance Pentests We Cover
HIPAA Penetration Testing
Healthcare apps + ePHI systems
SOC 2 Penetration Testing
Type I & Type II audit-ready
PCI DSS Penetration Testing
Cardholder data environments
ISO 27001 Penetration Testing
ISMS-aligned testing
NIST 800-53 Penetration Testing
Federal control mapping
CMMC Penetration Testing
DoD contractor compliance
FedRAMP Penetration Testing
Government cloud auth
All Compliance Frameworks
Pick your framework
Quick FDA Pentest Questions
Medical Device Penetration Testing Services
Every compliance pentest pulls from these test-type services as needed. Scope is sized to your environment, not padded with hours.
Get Your FDA Pentest Scoped in 24 Hours
Share a few details and we'll follow up within one business day.
Rather skip the form?
Book a 30-minute scoping call instead